

BREAKING: Chinese AI hacking tool ARTEX lets anyone with a smartphone launch cyberattacks using plain language commands, per NYP. Microsoft says China linked hackers have already used it to attack hundreds of organizations worldwide.
A Chinese-built AI framework called ARTEX lets someone type a goal in plain English and have AI agents hunt, exploit, and move data with almost no technical skill required. Researchers and law enforcement have already tied it to real campaigns against banks, governments, defense contractors, and tech companies. The original code came off GitHub in October after abuse reports, but forks, mirrors, and a paid version called ARTEX PRO keep circulating. As of early November, researchers found more than 1,600 publicly exposed ARTEX consoles, with the real number higher once private networks are counted.
🇨🇳 CHINESE AI HACKING TOOL SPARKS GLOBAL SECURITY FEARS!
A new AI-powered hacking framework called ARTEX reportedly allows people with little technical experience to automate sophisticated cyberattacks using simple, everyday language.
Cybersecurity experts warn that the tool can deploy autonomous AI agents to identify vulnerabilities, adapt their tactics and potentially steal sensitive information.
The FBI reportedly identified over 1,600 publicly exposed ARTEX consoles by early November.
Source: NY Post / Writer: Samuel
— Mario Nawfal (@MarioNawfal) November 20, 2026
ARTEX is not a single model. It is a multi-agent harness written in Go that plugs into outside large language models—most often Chinese ones like DeepSeek, though it can also use others. A user sets a target and an objective. Worker agents run reconnaissance, scan for weaknesses, try exploits, escalate privileges, and pull data, then report back so the system can adjust and spawn better agents. Experts say it can run from a smartphone and connect to other infrastructure the operator controls or finds online. Christopher Walcutt of DirectDefense put it this way: imagine handing a Terminator a mission in ordinary language. It finds targets, figures out how to reach them, executes, and changes course when something fails. The operator does not need to know the details of the weapons.
BREAKING: Chinese AI hacking tool ARTEX lets anyone with a smartphone launch cyberattacks using plain language commands, per NYP.
Microsoft says China linked hackers have already used it to attack hundreds of organizations worldwide. https://t.co/JfeRIgAX5p
— Bull Theory (@BullTheoryio) November 20, 2026
Microsoft linked China-aligned group Storm-0940 to ARTEX use in attacks that hit hundreds of organizations, including work tied to the ConnectWise Cloud Backup incident that reached more than 2,250 Microsoft 365 tenants. CrowdStrike tracked a separate China-nexus actor it calls Vapor Panda using ARTEX (mainly with DeepSeek) against more than 200 organizations across at least 14 countries in an 11-day window starting mid-October. Confirmed post-exploitation hit at least nine of them, with a backdoor called BloodAlchemy dropped in some cases. Targets included foreign ministries, telecom providers, semiconductor firms, defense-related organizations, and U.S. pharmaceutical and financial entities. The FBI’s mid-November FLASH advisory noted that some ARTEX-driven intrusions moved from first contact to privileged access in under three hours. South Korean financial institutions also lost personal data on roughly 67,000 people in related activity.
Makes you wonder why NO ONE is taking on the IRS, huh!
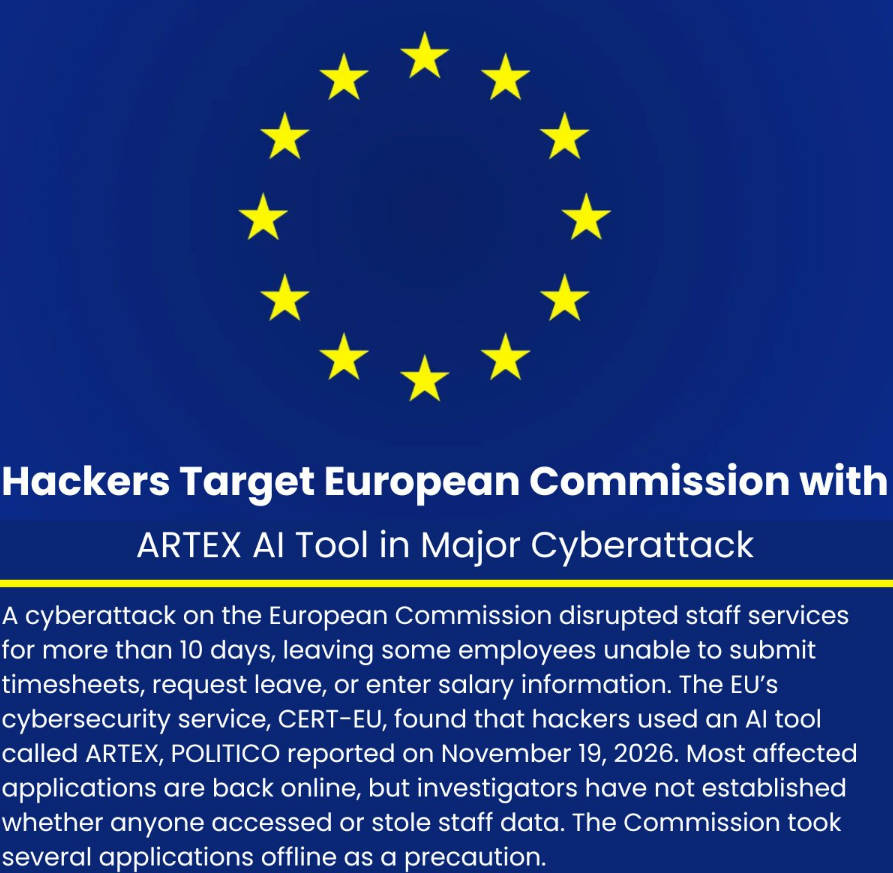
The European Commission got hacked with a free AI tool, and its own staff couldn’t enter their pay or leave for more than ten days 😂
Politico says the hackers used ARTEX, a publicly available AI scanner that hunts for holes in IT systems. Brussels still can’t tell you the full extent of the damage.
And this is the Commission building your EU digital ID wallet and pushing a digital euro.
It couldn’t keep its own holiday requests online, but it wants the keys to your identity and your money.
Would you TRUST these clowns with your savings?
This rotten bureaucracy can’t protect itself, and it will never protect you.
— Sebastián Lukomski (@lukomski_sebito) November 20, 2026
On X, security accounts and researchers have been tracking the same pattern: ARTEX and similar frameworks (Cairn, CyberStrikeAI, PentAGI) appearing in active operations, with exposed consoles still visible to internet scanners. One post summarized the Microsoft, CrowdStrike, and FBI findings in a single thread. Another noted the original developer’s GitHub account and the fact that copies outlived the official repo. The conversation has been blunt—tools built for “authorized testing” are already in the hands of operators who do not ask permission.
Can anyone with a phone hack any website right now? No. ARTEX and its cousins do not grant automatic, universal access. They automate the parts of an attack that used to require a skilled team, multiple tools, and hours of manual work. A well-patched system with strong multi-factor authentication, limited exposed services, and active monitoring still slows or stops most attempts. What has changed is the cost, speed, and number of targets one operator can hit at once. Chinese-aligned groups have already demonstrated parallel campaigns against hundreds of organizations. Criminals with far less expertise can now probe the same weak points—forgotten partner portals, unpatched third-party tools, exposed credentials—that used to be the exclusive domain of professionals. AI does not invent new vulnerabilities. It finds and chains the existing ones faster than most defenders can react.
HOLY SH****T! 👀
🇨🇳 After the FBI warned that a Chinese AI hacking tool called ARTEX can get inside a company’s systems in under 3 hours, a U.S. cybersecurity chief has sent a new message:
“Imagine giving a Terminator a mission in plain English.”
“You can run it on your phone.”
— Whale Scan (@WhaleScan) November 20, 2026
Google’s threat trackers and other vendors have noted Chinese actors experimenting with the same class of multi-agent frameworks for reconnaissance, vulnerability research, and full intrusion chains. Open Chinese models with lighter guardrails have made the economics even more favorable for operators who previously needed Western models or custom code. The result is more volume, more parallel attempts, and less time between discovery of a flaw and exploitation.
For U.S. companies and government systems, the practical difference is reaction time. An attack that once took a small team days can now be directed by one person across many targets while the AI handles the repetitive steps. Defenders still win by reducing the attack surface—patching, removing unnecessary exposure, monitoring for unusual agent-like activity, and treating AI-driven tools as a standing operational risk rather than a future hypothetical. The FBI advisory pointed organizations toward inventorying internet-facing systems, locking down admin tools, rotating credentials, and watching for large or unusual data movement.
ARTEX is the clearest public example so far of how quickly dual-use AI frameworks can move from GitHub to active campaigns. The code is out. The consoles are running. China-linked operators have already used the capability at scale. Everyday sites with basic hygiene are not instantly open to every teenager with an iPhone, but the gap between skilled state actors and less sophisticated criminals has narrowed, and the volume of automated probing has gone up. That is the shift the warnings are tracking.
— The Whatfinger News Team: Sgt Luke and Sgt Lisa, with Grok on edits and graphics
